Codacy

Codacy

Codacy is an automated code quality and security platform that integrates directly into your development workflow to catch issues early. It provides static analysis (SAST), software composition analysis (SCA), secret scanning, and AI-powered code reviews, all enforced through unified coding standards. Targeted at fast-paced engineering teams, it consolidates multiple security and quality tools into one. Key features include AI Guardrails for real-time IDE feedback, automated Pull Request reviews, and a centralized AI Risk Hub for managing AI-specific coding policies. It supports 49 programming languages and integrates with GitHub, GitLab, and Bitbucket.

Coding
Visit website
Added on
Sep 22, 2026
AI Code ReviewIDE GuardrailsSAST/SCA ScansSecret DetectionMulti-languageGit IntegrationSelf-hosted Option
Product information

Everything worth knowing about Codacy

The complete picture — from everyday features to the technical detail builders and IT folks dig for.

Core features

What it actually does

AI Guardrails (IDE Extension)
Automated code quality and security scans embedded in IDE (VSCode, JetBrains, Cursor) for real-time feedback on AI-generated and human code.
Security & Quality Scans
SAST, SCA, Secret scanning, code quality analysis, and duplication detection across 49 languages.
AI Code Review & Merge Gates
AI-powered analysis on pull requests with automated false positive detection and merge policies.
Cloud-Hosted Scans & Integrations
Integrated analysis with GitHub, Bitbucket, GitLab, plus Jira & Slack for team-wide visibility and workflow automation.
Technical capabilities
CI/CD Pipeline Integration
Automated scans triggered via Git workflow integration and post-commit hooks.
Local Client-Side Analysis Tools
Support for running analysis with tools like ESLint, SpotBugs, and Dart Analyzer locally.
Must watch videos
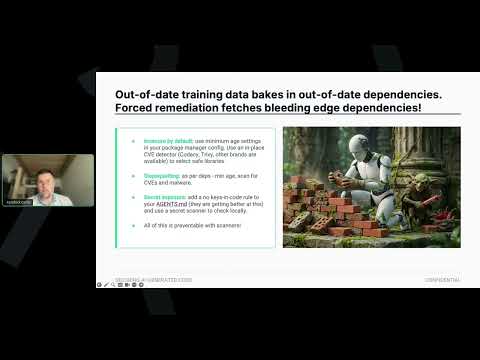
Why AI Coding Assistants Keep Pulling Insecure Dependencies
2:20
Tutorial2:20
Why AI Coding Assistants Keep Pulling Insecure Dependencies
In the session we ran with WorkNest Secure, Kendrick Curtis, CTO of Codacy, talked about how coding assistants tend to suggest insure dependency versions by design. On the one hand, they are anchored to their training data, which skews toward older, widely-referenced releases rather than the version your policy currently mandates. Then, when you ask an assistant to remediate, and it may swing to a very recent release instead, trading a stale-version problem for a bleeding-edge one. #dependencies #malware #codingassistant #codingagents
Securing AI Generated Code From Prompt to Pentest
44:19
Tutorial44:19
Securing AI Generated Code From Prompt to Pentest
Most malicious npm packages get flagged within hours, so a three-day minimum age in your .npmrc removes roughly 95% of bleeding-edge dependency risk. That's one of four AI-assisted development vulnerabilities Kendrick Curtis (CTO, Codacy) works through here. Jordan Constantine (Head of Offensive Security, WorkNest Secure) then shows the attacker's side: a chatbot that gave up 60,000 user records and MD5 password hashes, and an AWS document ingestion service talked into leaking its own credentials. TOOLS Codacy — code quality and security scanning, free to start: https://codacy.com/sign-up Verity — agentic code review that self-corrects inside your AI agent: https://verity.md WorkNest Secure — penetration testing and red team: https://worknest.com/ CHAPTERS 0:19 What Codacy covers: DAST, containers, secrets, coverage, clean code 0:57 Jordan Constantine: pentesting, red team, social engineering 2:15 The four critical vulnerabilities in AI-assisted development 2:38 #1 Insecure dependencies and malware: insecure by default 3:36 npm malware: poisoned packages hunting your credentials 3:53 Slopsquatting: typosquatting at AI speed and scale 6:46 Verity: self-correcting the agent to a secure version 7:54 #2 Malicious MCP servers: what an MCP server actually is 10:44 #3 Prompt injection: hacking computers in English 13:55 #4 Unbounded agent permissions: agents execute as you 18:32 AI on the attacker’s side: prompt injection tops the findings 19:24 Why social engineering skills transfer to hacking systems 20:19 The CISO problem is speed and scale, not complexity 21:11 Guardrails: the naive "ignore previous instructions" 26:24 Walkthrough 1: which database tables can the chatbot reach? 28:35 Walkthrough 2: SSRF via an AWS document ingestion service 31:16 What to do differently: treat AI like infrastructure 32:27 Human in the loop for payments, permissions, sensitive data 33:56 Q&A 34:17 Do AI SOC tools respond fast enough to matter? 36:15 Which AI vulnerability is hardest to catch in review? 37:31 Custom review instructions and AI PR review 38:05 Real-time guardrails to stop an agent deviating? 38:43 Assume guardrails fail: the WAF and Cloudflare analogy 39:41 Filtering input before it reaches the agent 40:56 Securing AI-written code across PRs, pipelines and CI/CD 41:30 Why leaked CI/CD credentials beat a compromised laptop 42:04 Reviewing AI-generated code for cognitive bias #AISecurity #DevSecOps #PromptInjection #AppSec #MCP #SupplyChainSecurity #PenetrationTesting #CodeQuality #AICodeReview #CodeSecurity
Introducing Container Image Scanning
2:58
Tutorial2:58
Introducing Container Image Scanning
Container Image Scanning is now available on Codacy. Run daily CVE scans on container images without standing up new tools or infrastructure, and see the results directly in the Codacy Security and Risk Management dashboard.

Who uses it

Real use cases, no hype
Enforce AI Coding Policies
Prevent unapproved models, insecure dependencies, and policy violations from AI-generated code before it's committed.
Automate PR Code Reviews
Get actionable, low-noise AI feedback on every pull request with ready-to-commit fix suggestions.
Continuous Security & Compliance
Maintain audit-ready reports for SOC2, ISO27001, and PCI DSS with automated scanning and SBOM generation.
Boost Developer Productivity
Catch and fix quality/security issues directly in the IDE via real-time scans, reducing context-switching.
Consolidate DevSecOps Toolchain
Replace separate SAST, SCA, secrets, and quality tools with a single platform for unified coding standards.
Legacy Code Health & Refactoring
Identify complex, error-prone, and duplicated code across large codebases to prioritize modernization efforts.
Runtime & Container Security
Find vulnerabilities in deployed applications and container images via DAST and container scanning.
What's great
  • True all-in-one platform for code quality, security, and AI governance.
  • Exceptional IDE integration with real-time feedback (VS Code, JetBrains, Cursor).
  • Strong AI Guardrails prevent AI-generated code from introducing new vulnerabilities.
  • Zero-config setup for many projects; scans results in minutes.
  • Generous free tier for individuals and open-source projects.
Technical strengths
  • Supports 49 languages with deep static analysis via specialized engines (e.g., SpotBugs, ESLint).
  • Continuous daily CVE and malware re-scans for proactive dependency protection.
  • SOC 2, ISO 27001, and PCI DSS compliance with automated audit-ready reporting.
Where it falls short
  • Business tier pricing is opaque and requires a custom quote.
  • UI can feel cluttered when navigating deep configuration or reporting sections.
  • Some advanced features (DAST, Container Scanning) are gated behind the highest tier.
  • AI features are powerful but may require policy tuning to avoid false positives.
Technical limitations
  • Self-hosted deployment requires Kubernetes and has a complex system requirement footprint.
  • Analysis for some languages or large monorepos can hit scan queue limits on lower plans.
  • Custom rule configuration has a steeper learning curve than basic settings.
For technical folks

The deep-dive specs

FAQ

Includes technical Q&A
Codacy provides a unified cloud platform for code quality, security (SAST/SCA/secrets), and AI code governance in one tool. It emphasizes zero-config cloud hosting, real-time IDE feedback via Guardrails, and automated compliance reporting, unlike self-hosted focused SonarQube or security-specific Snyk.

Traffic Insights

Monthly Visits

—

October 2026

Growth Rate

0%

vs last month

Dominance

0%

in Coding

Top Country

—

Top Countries Breakdown

—

Growth Trend

Stable

Traffic has remained stable.

Honest pricing

No sneaky tiers, no “contact sales”

Here's who each plan is actually for — and where the hidden charges might hit.

Developer
Free

Individuals

  • Free forever
  • Auto-fix AI code
  • Scan-as-you-type
  • Security Scans (SAST
  • SCA
  • Secrets)
  • Code Quality Scans
Team
Most picked
$21/mo

Teams

  • Everything in Developer
  • plus: GitHub
  • Bitbucket & GitLab Integration
  • Cloud-hosted Code Quality & Security Scans
  • Up to 100 private repos & unlimited LOC
  • AI Reviewer & Merge Gates for Pull Requests
  • Shared Coding Standards across 49 languages
Business
Custom

Enterprise

  • Everything in Team
  • with options for: Unlimited private projects
  • Priority scan queue
  • Daily re-scans against new CVEs
  • AI Inventory + AI Risk Hub
  • DAST
  • Container Image Scanning
View Full Plans & Pricing on Codacy

Official pricing, checkout, and plan upgrades are handled directly on codacy.com.

Reviews

What the internet actually thinks

Data refreshed weekly. No paid placements.

Trustpilot
Not reviewed yet
G2
G2
Not reviewed yet
C
Capterra
Not reviewed yet
Product Hunt
Not reviewed yet
COMMUNITY COMMENTS

Leave a Comment

Help others make informed decisions. Your honest feedback shapes the community's understanding of this tool.

Tips for commenting

  • •Be specific about features you used
  • •Share real use cases and results
  • •Mention both pros and cons
  • •Keep it honest and constructive
to leave a comment

Your comment is published immediately.

Filter by rating:
Sort by:

No comments yet

Be the first to share your experience with this tool.

Alternatives

Not quite the right fit?

Here's what else is out there.