Sweet Security

Sweet Security

Sweet Security provides a Runtime Cloud-Native Application Protection Platform (CNAPP) and AI Security Platform (AISP) focused on real-time threat detection, response, and enforcement for cloud workloads and autonomous AI agents. It uses eBPF-based agents to analyze runtime events at machine speed, identifying exploitable attack paths and blocking threats the moment they act without performance degradation. Key capabilities include Cloud Application Detection & Response (CADR), Cloud Security Posture Management (CSPM), Identity Threat Detection and Response (ITDR), and API Security. Its core is a proprietary Learning Loop that continuously tests environments against zero-day threats, learns normal behavior, and turns fixes into inline runtime guardrails. The platform is designed for security teams operating at scale, aiming to replace noisy vulnerability scanners with actionable, high-fidelity findings.

Automation
Visit website
Added on
Sep 21, 2026
Runtime CNAPPAI SecurityeBPF agentAttack path analysisReal-time enforcementCloud & AI unified
Product information

Everything worth knowing about Sweet Security

The complete picture — from everyday features to the technical detail builders and IT folks dig for.

Core features

What it actually does

Runtime Cloud & AI Security
Proactive enforcement and threat detection for cloud workloads and AI agents in production runtime.
Continuous Learning Loop
AI-driven cycle that learns normal application behavior to automatically improve defenses against new threats.
One-Click Runtime Guardrails
Turns a vulnerability fix or threat response into an inline enforcement rule to prevent recurrence.
Unified Cloud & AI Platform
Single platform for managing security across all cloud applications, APIs, and autonomous AI agents.
Technical capabilities
eBPF-Based Agent Architecture
Uses lightweight, efficient eBPF technology for deep runtime monitoring without performance degradation.
AI-Verified Attack Path Analysis
Automates the discovery of exploitable attack paths with high accuracy, prioritizing critical risks.
High-Volume Event Analysis
Processes over 1 billion runtime events per day for comprehensive visibility.
Must watch videos
Sweet Security: Transforming Cloud Security. Defining AI Security.
1:48
Tutorial1:48
Sweet Security: Transforming Cloud Security. Defining AI Security.
Founded by the former CISO of the IDF (Israel Defense Forces) and a team of elite experts in offensive and defensive cloud security, Sweet is offering a new flavor of CNAPP (Cloud-Native Application Protection Platform). Learn more at https://sweet.security Sweet prioritizes resilient cloud protection that stops cloud attacks and delivers the strongest line of defense in an ever-evolving landscape. Leveraging unified cloud visibility, deep runtime context, and cutting-edge cloud-native technologies, Sweet empowers security teams to detect and neutralize real-time threats as they happen. “The cloud security category is in the early innings of growth, and Sweet brings a disruptive technology to the runtime space, enabling companies to better protect their cloud infrastructure,” says Richard Seewald, founder and Managing Partner at Evolution. Evolution Equity Partners is an international venture capital investor led by technology entrepreneurs who have built software companies around the world and who leverage tremendous operating, technical, product development and go-to-market expertise to help entrepreneurs win. About: https://evolutionequity.com Subscribe to Cybercrime Magazine on YouTube ➤ https://bit.ly/cybercrimemagazine Listen to the Cybercrime Magazine Podcast ➤ https://soundcloud.com/cybercrimemagazine Tune into WCYB Digital Radio ➤ https://cybercrime.radio Get more Cybercrime Magazine media ➤ https://cybersecurityventures.com/ Follow Cybercrime Magazine / Cybersecurity Ventures: LinkedIn ➤ https://www.linkedin.com/in/cybersecuritysf/ X ➤ https://twitter.com/CybersecuritySF Instagram ➤ https://www.instagram.com/cybercrimemagazine/ #cybersecurity #hacker #ai #cybercrime #jobs #recruiting #womenintech #cloudsecurity
Sweet Security Review: Runtime-Powered CNAPP Explained
8:20
Review8:20
Sweet Security Review: Runtime-Powered CNAPP Explained
Your company is in the market for a runtime-powered CNAPP and you've heard of Sweet Security. You're wondering if they use AI, and how do they use it? Sweet Security positions itself as a runtime-powered Cloud-Native Application Protection Platform, designed to watch your applications and cloud workloads while they are actually running. Traditional CSPM and code scanners are valuable before deployment, but they can miss fast-moving threats and zero-days that emerge in production. By focusing on real-time protection, Sweet Security aims to detect and stop risks as they unfold across containers, Kubernetes, serverless, and virtual machines in AWS, Azure, and Google Cloud. Do they use AI? Runtime analytics in modern CNAPPs typically leverage machine learning techniques for anomaly detection, behavior profiling, and automated correlation. Expect capabilities that learn normal patterns for processes, identities, and network flows, then surface suspicious deviations with high-priority alerts. As with any vendor, confirm details during your proof of concept: models used, data sources, explainability, false-positive handling, and how detections map to MITRE ATT&CK. Core capabilities to look for include runtime threat detection and response, workload and container protection, Kubernetes visibility, and posture management that ties misconfigurations to live exploitation risk. Many buyers also evaluate identity insight similar to CIEM, attack path analysis, and exposure scoring that blends CSPM findings with runtime signals. Integrations with SIEM and SOAR platforms, ticketing tools like Jira and ServiceNow, and messaging tools such as Slack or Microsoft Teams are common and reduce operational friction. How it works in production: a runtime-first platform typically ingests cloud-native telemetry like AWS CloudTrail, VPC Flow Logs, GuardDuty findings, Azure Activity Logs, Microsoft Defender for Cloud alerts, GCP Audit Logs, and Kubernetes audit events. It may add lightweight sensors at the node or container layer, often using Linux eBPF to observe process, file, and network activity with minimal overhead, or it can operate agentless for certain use cases via cloud APIs. The goal is to correlate signals in real time so security teams can see lateral movement, privilege misuse, suspicious outbound traffic, and attempts to exploit zero-day vulnerabilities even when no patch exists yet. Pricing and packaging are typically subscription-based SaaS, tiered by factors such as number of workloads or nodes, cloud accounts, data volume, and retention. Expect enterprise options for SSO, RBAC, audit logging, and support SLAs. The best path is to request a scoped trial or POC that includes high-fidelity test scenarios, deployment to a non-production Kubernetes cluster like EKS, AKS, or GKE, and measurable success criteria around alert quality and mean time to detect. How does Sweet Security compare to other cloud security vendors like Wiz, Palo Alto Networks Prisma Cloud, Orca Security, Lacework, and CrowdStrike Falcon Cloud Security? Its differentiation is the runtime-first strategy. If your priority is catching active threats in production and shrinking alert noise by adding live context to posture findings, a runtime-powered CNAPP can be compelling. If your immediate need is breadth of posture checks or compliance-only reporting, more traditional CSPM-led tools may be sufficient, but adding runtime context usually improves prioritization and response. Who should consider it? Teams running Kubernetes, microservices, and serverless at scale, organizations with strict compliance needs such as PCI DSS, SOC 2, HITRUST, or financial services standards, and any enterprise that wants to merge shift-left security with runtime detection and response. Key questions for vendors include: multi-cloud depth, Kubernetes coverage, data residency, performance overhead, integration breadth, and the transparency of AI-driven detections. Video Chapters - 00:00 Does Sweet Security use AI? - 01:35 What is Runtime-Powered CNAPP? - 03:10 Core Capabilities - 05:02 How it Works in Production - 06:28 Integrations and Deployments - 07:45 Pricing and Packaging - 09:02 Pros and Cons vs Competitors - 10:40 Who Should Buy - 11:30 Demo and Next Steps #CloudSecurity #CNAPP #RuntimeSecurity #Kubernetes #DevSecOps More information on stackinsight.net/sweet-security-review
CDR Demo: Sweet Security at the CDR Showdown 2025
27:36
Tutorial27:36
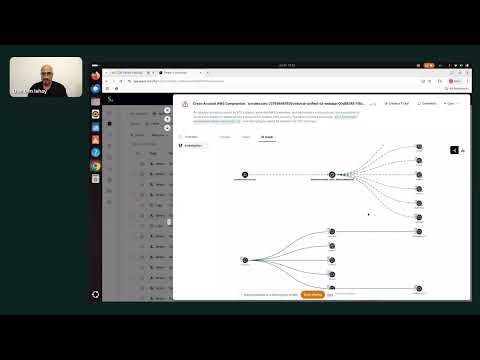
CDR Demo: Sweet Security at the CDR Showdown 2025
As part of Tamnoon’s CDR Showdown, Orel Ben Ishay, VP of R&D at Sweet Security, delivers a full live demo of our Cloud Detection and Response (CDR) capabilities. See how Sweet Security unifies runtime visibility, AI-powered threat detection, and rapid response across the entire cloud stack. In this session, Orel demonstrates how our CDR detects advanced threats in real time, correlates activity across the attack chain, and provides the context and tooling to investigate and respond fast. Whether you’re in cloud security, incident response, or DevSecOps, this Tamnoon-hosted showcase reveals how Sweet Security helps you stay ahead of modern cloud attacks.

Who uses it

Real use cases, no hype
Runtime Threat Detection & Response
Block active threats in cloud workloads and AI agents in real-time.
Continuous Cloud Security Posture
Automate runtime CSPM to fix misconfigurations where they matter.
AI Agent Security
Secure autonomous AI agents by tracing and blocking malicious actions inline.
Vulnerability Prioritization
Cut through noise to fix only vulnerabilities on real, exploitable attack paths.
Identity Threat Detection
Detect and respond to identity-based attacks moving laterally in the cloud.
Offensive Security Validation
Continuously test your environment with simulated attacks to find gaps.
SOC & IR Efficiency
Provide SOC teams with prioritized, actionable alerts with zero white noise.
What's great
  • Rapid deployment, securing an organization in under 2 hours
  • High accuracy (>99%) with AI-verified findings, reduces false positives
  • Unified platform for both cloud (CNAPP) and AI agent security
  • Prioritized attack paths for actionable, immediate remediation
Technical strengths
  • Runtime eBPF-based enforcement is lean and low-overhead
  • Integrated Learning Loop™ for continuous attack and defense improvement
  • Inline AI guardrail enforcement at machine speed (<100ms)
Where it falls short
  • Primarily a cloud/AI runtime focus; limited traditional endpoint story
  • Primarily SaaS delivery model; no self-hosted option mentioned
  • Pricing and contract terms are not transparent; requires a demo
  • Could be overkill for small, non-cloud-native teams
Technical limitations
  • Requires eBPF support in the kernel, which may not be available everywhere
  • Deep runtime instrumentation requires careful production rollout planning
  • Dependency on proprietary 'Learning Loop' for ongoing defense evolution
For technical folks

The deep-dive specs

FAQ

Includes technical Q&A
Sweet operates at runtime using eBPF, analyzing live behavior instead of just static configs or perimeter logs. It enforces policies inline, blocking threats as they execute, not just alerting on them.

Traffic Insights

Monthly Visits

—

October 2026

Growth Rate

0%

vs last month

Dominance

0%

in Automation

Top Country

—

Top Countries Breakdown

—

Growth Trend

Stable

Traffic has remained stable.

Pricing overview
Paid Pricing

Sweet Security Pricing

Sweet Security uses a paid pricing structure. Real-time rates, custom enterprise quotas, and plan details are managed directly on their official platform.

Check Pricing on Sweet Security
Reviews

What the internet actually thinks

Data refreshed weekly. No paid placements.

Trustpilot
Not reviewed yet
G2
G2
Not reviewed yet
C
Capterra
Not reviewed yet
Product Hunt
Not reviewed yet
COMMUNITY COMMENTS

Leave a Comment

Help others make informed decisions. Your honest feedback shapes the community's understanding of this tool.

Tips for commenting

  • •Be specific about features you used
  • •Share real use cases and results
  • •Mention both pros and cons
  • •Keep it honest and constructive
to leave a comment

Your comment is published immediately.

Filter:
Sort:

No comments yet

Be the first to share your experience with this tool.

Alternatives

Not quite the right fit?

Here's what else is out there.