Nozomi Networks

Nozomi Networks

Nozomi Networks provides AI-driven cybersecurity solutions for operational technology (OT), industrial control systems (ICS), and IoT environments. Its platform offers continuous monitoring, asset inventory management, threat detection, and risk assessment across critical infrastructure. Key capabilities include passive and active network monitoring, behavioral anomaly detection, and integration with major security tools. The solution is designed for organizations managing complex industrial networks, such as utilities, manufacturing plants, and transportation systems. It helps identify vulnerabilities, prioritize risks, and respond to threats without disrupting operations. The platform supports cloud, on-premises, and hybrid deployments.

Automation
Visit website
Added on
Sep 18, 2026
OT/IoT SecurityAsset InventoryThreat DetectionAI AnalyticsPassive MonitoringIndustrial ProtocolsGlobal Installations
Product information

Everything worth knowing about Nozomi Networks

The complete picture — from everyday features to the technical detail builders and IT folks dig for.

Core features

What it actually does

OT & IoT Asset Discovery and Inventory
Identifies every connected device (OT, IoT, IT) across your environment, mapping assets, their behavior, and context in real-time to establish a foundational inventory.
Continuous Threat Detection & Anomaly Monitoring
Detects cybersecurity threats and process anomalies without manual alert sorting, using AI-driven analysis to pinpoint critical issues in industrial networks.
AI-Powered Risk Prioritization and Response
Provides prioritized remediation guidance to quickly respond to emerging cyber risks, helping to efficiently increase resilience and reduce operational risk.
Passive & Active Network Monitoring
Supports passive monitoring for asset inventory and threat detection, alongside safe active polling and wireless monitoring for comprehensive visibility.
Technical capabilities
Integration with Security Ecosystem
Connects with a wide range of security and networking tools through a technology alliance ecosystem to enhance existing workflows and visibility.
OT Protocol Analysis & Deep Packet Inspection
Specialized analysis of industrial protocols (e.g., Modbus, PROFINET) and network traffic for accurate asset identification and threat detection in OT environments.
Must watch videos
Nozomi Hour | December 2025 | The AI Inflection Point
37:17
Tutorial37:17
Nozomi Hour | December 2025 | The AI Inflection Point
Hear the latest OT/IoT/CPS cybersecurity updates and insights from our industry expert Anton Shipulin. Anton will discuss the latest developments in the OT/IoT threat landscape and show you how to take full advantage of the Nozomi Networks platform, your best defense against current and future cyber threats. In this information-packed session, you’ll learn about: - Recent security incidents, vulnerabilities, and emerging attack techniques targeting OT and IoT - Evolving regulations, standards, compliance frameworks, and best practice guidance - Cutting-edge tools and technologies trends in OT/IoT security
The Journey to Wireless Security in OT Environments
34:58
Tutorial34:58
The Journey to Wireless Security in OT Environments
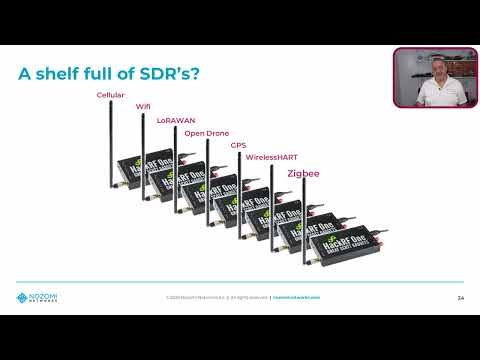
What it would take to engineer and implement a wireless communication security solution? Marty the OT Guy walks you through the process and some of its hurdles. On the way, we look at some statistics and metrics that help inform why this securing wireless communications is so important. This video is a practice run of a presentation from the 2025 NZ OT ICS Summit where Marty covered the challenges, benefits and solutions to today's wireless security landscape.
Building Cyber Resilient OT Systems — IEC 62443 in Practice
53:25
Tutorial53:25
Building Cyber Resilient OT Systems — IEC 62443 in Practice
As cyber threats to operational technology rise, organisations across the Asia-Pacific are under growing pressure to strengthen OT security. IEC 62443 — the internationally recognised standard for securing industrial automation and control systems (IACS) — has become the global benchmark for managing industrial cybersecurity risk. Regulators across the region, including Australia’s critical infrastructure legislation, are increasingly adopting or aligning with IEC 62443. For OT security teams, applying these standards is now essential for both compliance and resilience. In this webinar, experts from Nozomi Networks and ABB will share practical guidance on IEC 62443 and how to overcome the challenges of implementation. Watch now to: - Gain a practical understanding of IEC 62443 and why it matters. - Learn how to operationalise IEC 62443 in your region. - Hear real-world success stories: how enterprises are applying segmentation, defense-in-depth, and secure lifecycle strategies.

Who uses it

Real use cases, no hype
Critical Infrastructure Protection
Secures power grids, water treatment, and oil & gas operations from cyber threats that could disrupt physical processes.
Industrial Asset Inventory
Automatically discovers and classifies all OT/IoT devices across heterogeneous industrial networks.
Threat Detection & Response
Detects malicious activity and process anomalies in real-time, providing prioritized response guidance.
Compliance Reporting
Simplifies meeting NERC CIP, NIS2, TSA, and other regulatory requirements for industrial cybersecurity.
IT/OT Convergence Security
Provides visibility and control as traditional IT networks connect with operational technology systems.
Data Center IoT Security
Protects the growing number of IoT devices within data center environments from being compromised.
Industrial Vulnerability Management
Identifies and prioritizes vulnerabilities across OT assets without disruptive active scanning.
What's great
  • Leader in OT/IoT security with 100% customer retention
  • AI-driven asset intelligence and threat detection
  • Broad compliance support (NERC CIP, NIS2, etc.)
  • Scalable to 100M+ monitored devices
Technical strengths
  • Passive network monitoring is non-disruptive to OT operations
  • Proprietary Vantage IQ AI engine for behavior baselining
  • Deep packet inspection for industrial protocols (e.g., Modbus, S7comm)
Where it falls short
  • Complex deployment requires specialized OT/IoT expertise
  • High cost typical of enterprise-grade OT security solutions
  • Heavy reliance on passive monitoring may miss certain endpoint threats
Technical limitations
  • Proprietary sensor ecosystem (Guardian/Arc) creates vendor lock-in
  • Limited effectiveness on legacy or air-gapped OT networks
For technical folks

The deep-dive specs

FAQ

Includes technical Q&A
OT cybersecurity focuses on protecting the hardware and software systems that control physical processes in industries like manufacturing, energy, and utilities, where disruptions can have real-world consequences.

Traffic Insights

Monthly Visits

—

October 2026

Growth Rate

0%

vs last month

Dominance

0%

in Automation

Top Country

—

Top Countries Breakdown

—

Growth Trend

Stable

Traffic has remained stable.

Pricing overview
Paid Pricing

Nozomi Networks Pricing

Nozomi Networks uses a paid pricing structure. Real-time rates, custom enterprise quotas, and plan details are managed directly on their official platform.

Check Pricing on Nozomi Networks
Reviews

What the internet actually thinks

Data refreshed weekly. No paid placements.

Trustpilot
Not reviewed yet
G2
G2
Not reviewed yet
C
Capterra
Not reviewed yet
Product Hunt
Not reviewed yet
COMMUNITY COMMENTS

Leave a Comment

Help others make informed decisions. Your honest feedback shapes the community's understanding of this tool.

Tips for commenting

  • •Be specific about features you used
  • •Share real use cases and results
  • •Mention both pros and cons
  • •Keep it honest and constructive
to leave a comment

Your comment is published immediately.

Filter:
Sort:

No comments yet

Be the first to share your experience with this tool.

Alternatives

Not quite the right fit?

Here's what else is out there.